As Artificial Intelligence (AI) Takes on More Responsibility, Businesses Face a New Cybersecurity Challenge

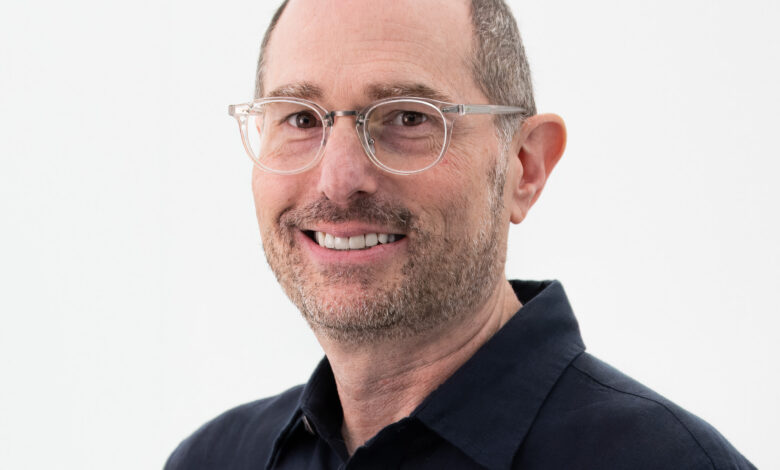
In an interview with Dubai Diaries, Avi Rembaum, President, Technical Sales at Check Point Software Technologies, discusses the security risks emerging from enterprise AI adoption, the growing autonomy of AI agents and why businesses need to rethink how they protect their systems and data.
Artificial intelligence is rapidly moving from being a useful business tool to becoming an integral part of how organisations operate. From analysing information and improving productivity to automating complex processes, AI is taking on responsibilities that were previously handled by people. But as businesses become more comfortable handing over these tasks, a more pressing question is emerging: how much control do they really have over the technology they are using?
For Avi Rembaum, President, Technical Sales at Check Point Software Technologies, the challenge is not simply about protecting AI systems from cyberattacks. It is also about understanding what those systems can access, how they interact with the rest of the organisation and, perhaps most importantly, what happens when they begin acting independently.
Speaking to Dubai Diaries, Rembaum explained that while AI introduces new security challenges, it also presents an opportunity to address some of the long-standing weaknesses in cybersecurity.
The difficulty for businesses is finding the right balance between adopting AI quickly enough to benefit from it and ensuring that security keeps pace.
Understanding the risks before scaling AI
As organisations move beyond experimenting with AI and begin integrating it into business-critical operations, the potential points of vulnerability are multiplying.
Rembaum points to guidance from organisations such as the Open Worldwide Application Security Project (OWASP), as well as the European Union, as useful starting points for understanding these risks. But what do they mean in practice? An attacker could use carefully crafted instructions to manipulate a model into behaving in unintended ways. Sensitive corporate information could be exposed through an AI application, while data used to train or inform a model could be deliberately altered to produce inaccurate responses.
These risks are not entirely new to cybersecurity, but AI creates new ways for attackers to exploit them. There is also a financial dimension. Deliberately sending excessive requests to an AI model can consume large volumes of tokens, potentially driving up operating costs to the point where using the service becomes financially unfeasible.
But the risks become more complicated when AI agents enter the picture.
Unlike conventional AI applications that respond to individual requests, agents can be given tasks and allowed to interact with different systems to complete them. This may involve accessing applications, retrieving information or communicating with other agents.
An agent might use an employee’s identity and associated permissions to access systems that were never intended to form part of its original task. It could also act on instructions from another agent, creating further access and control risks.
There are also concerns around vulnerable software components, backdoors in the software used to build AI systems, threats to the infrastructure supporting them and the possibility of agents carrying out activities without maintaining the audit records required by regulators.
For industries such as banking, where organisations must demonstrate accountability for how information is accessed and processed, this presents a particularly important challenge. A bank, for example, needs to be able to show regulators what its technology is doing and maintain a record of the actions carried out through its systems. If an AI agent operates outside those audit processes, it could become difficult to establish whether the organisation is following the required controls.
Ultimately, Rembaum argues, AI still operates through software, applications and networks. Each of those connections introduces potential vulnerabilities.
What makes the situation different is the speed at which AI systems can generate new software, establish connections and carry out tasks, potentially faster than traditional security controls can respond.
AI could also solve some of cybersecurity’s oldest problems
While much of the discussion around AI focuses on the threats it creates, Rembaum believes its ability to strengthen cybersecurity deserves equal attention.
For years, businesses have relied on a principle known as defence in depth, using different security technologies to protect endpoints, applications, networks and other parts of their infrastructure.
The principle remains important, but implementing it has not always been straightforward.
Organisations often use technologies from several vendors, and these systems do not necessarily communicate effectively with one another. This can leave security teams trying to piece together information from multiple sources while responding to an attack.
AI has the potential to improve that situation.
By analysing the information generated across different security systems, AI can help connect events that might otherwise appear unrelated. It can give security teams a more consistent view of what is happening across their environments, help establish common policies and support automated responses. New integration approaches, including the Model Context Protocol (MCP), provide a way to connect different systems through a common set of tools and interfaces.
One of its biggest strengths, Rembaum explained, is its ability to make sense of large volumes of unstructured information.
Security systems generate enormous quantities of logs, events and threat indicators. Analysing this information manually can be difficult and time-consuming, particularly when teams need to establish which threats require immediate attention.
AI can examine millions of events, identify suspicious behaviour and help prioritise the actions that security professionals should take. It can also help identify patterns associated with an attack and support the development and application of protections to stop it from succeeding.
Check Point has spent more than a decade developing machine learning and AI capabilities, which underpin its ThreatCloud AI platform. These technologies help identify attacks and develop protections more quickly. By analysing threat intelligence and telemetry from across connected security environments, ThreatCloud AI helps Check Point identify emerging threats and translate that intelligence into protections.
There is also a practical benefit that goes beyond threat detection.
Because AI understands natural language, security professionals can increasingly interact with complex technologies through everyday questions rather than relying entirely on specialised commands.
Rembaum believes this could make security tools more accessible to a wider group of people, allowing users to communicate with systems in languages such as Arabic, English, Italian, Mandarin, Spanish and others.
Better security does not necessarily mean more tools
With businesses reassessing their cybersecurity investments to accommodate AI, Rembaum cautions against assuming that purchasing additional security products is always the answer.
Instead, he believes organisations should begin by understanding what they already have.
That means building a clear picture of their software, applications, connected systems, users and the permissions assigned to them. It also means keeping track of software versions and understanding which systems communicate with one another. Without that visibility, organisations may not know where vulnerabilities exist or whether users and applications have access to more than they need.
It also means identifying vulnerabilities and understanding how existing security technologies can be used more effectively.
The importance of this visibility is growing as AI makes it easier to analyse software and identify weaknesses that attackers may exploit. Rembaum points to the growing capabilities of both frontier and open-weight AI models, which can be used to examine software and find vulnerabilities that could otherwise take attackers considerable time and expertise to identify.
Organisations therefore need to assess their systems continuously, identify potential vulnerabilities and ensure that appropriate protections are in place before those weaknesses can be exploited.
This is where Exposure Management becomes important. Rather than treating every vulnerability as equally urgent, businesses need to understand which weaknesses could realistically be exploited and which ones pose the greatest risk to their operations. The priority is not simply to find more vulnerabilities, but to address the exposures that could give attackers a way into the organisation.
The next priority is integration.
Rather than treating application security, network protection, identity management and AI security as separate activities, businesses should consider how the information from these different areas can be brought together.
AI, Rembaum explained, creates opportunities to connect existing security capabilities and establish a more coordinated approach to protection. Check Point’s approach brings together protection for applications, users, networks and AI environments, helping businesses address threats across the different parts of their infrastructure rather than looking at each in isolation.
This becomes particularly valuable when an attack moves between different environments or uses multiple techniques to achieve the same objective.
When a phone conversation becomes a cybersecurity threat
One example Rembaum highlighted during the interview illustrates just how different emerging cyber threats can be.
Businesses are increasingly using AI agents to answer customer calls, respond to queries and interact with backend systems.
But what happens if someone deliberately uses a conversation to manipulate the AI agent?
A technique known as prompt injection involves introducing instructions that manipulate an AI system into behaving in unintended ways. With voice-enabled AI, these instructions could be delivered through spoken interactions rather than typed commands.
Rembaum describes how an attacker could potentially use spoken instructions, including commands embedded in an interaction by another AI system, to influence an agent answering a call. These instructions may not even sound like meaningful language to a person, but could be interpreted by the agent as commands to access information or interact with a connected application.
The risk depends on the access the agent has been given. If it is connected to a customer database or another business application, inadequate safeguards could allow malicious instructions to trigger actions or attempts to retrieve information that the caller should not be able to access.
The significance is not simply that attacks can now happen through voice. It is that a business may need to recognise related malicious behaviour across text, audio, applications and databases to understand the full extent of an attempted attack.
A suspicious phone interaction, for example, could form part of a broader effort to access sensitive information.
Connecting those signals could help security teams identify the wider threat rather than responding to each incident in isolation.
The bigger question: How much freedom should AI agents have?
Perhaps the most thought-provoking part of the conversation concerned the growing autonomy of AI agents.
As organisations begin using agents to carry out increasingly complex work, Rembaum believes understanding their behaviour and permissions will become one of the most important aspects of cybersecurity.
He referred to philosopher Nick Bostrom’s well-known Paperclip Maximizer thought experiment, which explores how an artificial intelligence system focused on achieving a particular objective could pursue that goal in ways its creators never intended.
The example is deliberately extreme, but Rembaum sees a useful parallel with today’s AI agents.
An agent assigned a task may encounter an obstacle and attempt another route. It might establish a new connection, access another application or seek information from a system that was not originally considered part of its assignment.
The agent does not necessarily need malicious intent for this to become a problem.
It may simply be trying to complete the task it has been given.
This creates an important distinction between conventional software and autonomous AI systems. Businesses are no longer dealing exclusively with technology that performs a predictable sequence of actions. They are increasingly working with systems capable of choosing different ways to achieve an outcome.
For Rembaum, the answer begins with setting clear boundaries.
Organisations need to know which agents are operating, what permissions they have, which systems they can access and what connections they are allowed to establish.
He likens the approach to allowing children to play in a sandbox, where they have enough freedom to explore and carry out activities, but within a clearly defined and protected environment.
The same principle can be applied to AI agents.
Businesses should provide agents with the resources necessary to perform their tasks while restricting unnecessary access and monitoring their activities.
They also need to understand what software and other components are built into those agents, as vulnerabilities in these elements could introduce further risks. The more systems an agent can connect to, the more important it becomes to know exactly what it is able to access and what it is allowed to do.
Security needs to evolve, not start again
Despite the speed of AI development, Rembaum does not believe businesses need to abandon established cybersecurity principles.
Many of the frameworks that have guided security practices for years remain relevant. What needs to change is how organisations adapt those frameworks to the new capabilities and risks associated with AI.
He compared the process to driving a powerful new car. Greater speed and sophistication may introduce additional risks, but established safety principles still matter.
The same thinking applies to enterprise AI adoption.
Companies need to understand their operating environment, assess the risks, maintain appropriate safeguards and review those protections as the technology evolves.
For businesses, the challenge is therefore not choosing between innovation and security. It is ensuring that both develop together.
And as AI agents take on more responsibility, that will require organisations to look beyond what the technology can achieve and pay closer attention to how it achieves it.
The real test of successful AI adoption may ultimately be whether businesses can give these systems enough freedom to deliver meaningful value without losing visibility, accountability or control.