Securing Artificial Intelligence (AI) Transformation: Check Point’s Diego Arrabal on Cybersecurity Priorities Across EEMEA

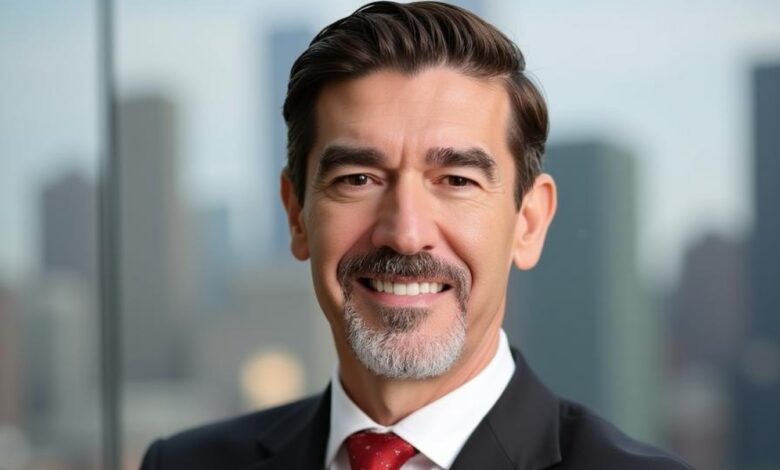
As artificial intelligence reshapes how businesses operate, organisations across the Middle East, Eastern Europe and Africa (EEMEA) are facing a common challenge: how to embrace new technologies without exposing themselves to greater cyber risks. Yet, with markets moving at different speeds and facing distinct security priorities, there is no single approach that works for everyone. In an exclusive interview with Dubai Diaries, Diego Arrabal, Vice President for EEMEA at Check Point Software Technologies, shares his perspective on the region’s evolving cybersecurity needs, the growing importance of prevention-first security and the changing role of channel partners. He also discusses why simplifying security environments and building protection into AI adoption from the outset will be central to helping businesses innovate and grow securely.
- Having taken on the leadership of Check Point’s EEMEA operations in July 2025, what have been your most significant observations about the region’s evolving cybersecurity landscape? How do customer priorities and security investment decisions differ across the Middle East, Eastern Europe and Africa, and what common challenges are emerging?
One of my biggest observations is that there is no single EEMEA cybersecurity market. The region brings together countries at very different stages of digital and economic development, each with its own priorities and challenges.
In the Middle East, significant investment in AI, data centres and digital infrastructure is creating demand for security that can support ambitious transformation programmes. Across Africa, rapid digitalisation is opening up new opportunities, while making it important to strengthen resilience, protect users and data, and develop local cybersecurity capabilities. In Eastern Europe, geopolitical realities continue to place a strong emphasis on protecting governments, critical infrastructure and essential services.
Despite these differences, a common challenge is emerging. Organisations are managing increasingly complex environments while facing threats that are becoming faster and more sophisticated. They need to modernise their security without adding further complexity. This makes prevention, visibility and the ability to apply consistent security across different environments more important than ever.
- Organisations across EEMEA are at different stages of AI adoption, with some markets moving rapidly towards enterprise-wide deployment while others are still establishing the necessary foundations. What are the biggest challenges businesses face in securing their AI transformation, and how should organisations balance the pressure to innovate with the need to manage emerging risks?
The biggest challenge is that AI adoption is moving faster than the security frameworks and governance processes designed to manage it. Employees are already using generative AI, sometimes without organisations having full visibility into what information is being shared. AI agents introduce another level of risk because they can access applications, interact with sensitive data and take actions on behalf of users. If their permissions are not properly controlled, they can create new routes into business-critical systems.
Organisations should not see security as something that comes after AI adoption. It needs to be part of the process from the beginning. That starts with understanding where AI is being used, protecting sensitive information, securing the applications and infrastructure involved, and applying clear controls over what AI systems and agents can access and do.
The principle of least privilege is particularly important. AI should have only the access it needs to perform its assigned tasks, with human oversight for sensitive decisions. The objective is not to slow down innovation, but to give organizations the confidence to accelerate AI adoption safely, because they understand and control the risks.
- As cyber threats become more sophisticated, the industry is increasingly emphasising prevention rather than relying primarily on detection and response. From a regional business perspective, are you seeing a meaningful shift in how organisations approach cybersecurity investment? What is driving this change, and what obstacles remain in translating prevention-first strategies into practice?
Yes, we are seeing a stronger recognition that detecting an attack after it has entered an organisation is not enough. Detection and response will always be important, but businesses would rather prevent an attack than have to manage its consequences.
AI is adding urgency to this shift. Attackers can use it to automate reconnaissance, identify weaknesses and create more convincing social engineering campaigns. The time available to identify and respond to an attack is becoming shorter. Organisations therefore need security that can identify and block threats before they develop into incidents.
However, moving to prevention-first security is not simply a matter of buying more technology. Many businesses have accumulated different security tools over the years, often operating in separate environments and without sufficient communication between them. This can leave gaps in visibility and make it harder to enforce consistent policies.
The priority should be to connect security intelligence, reduce complexity and focus on the exposures that present the greatest risk. Prevention needs to work consistently across networks, cloud environments, applications and users, rather than being treated as a series of separate measures.
- Channel partners and technology ecosystems play an important role in helping organisations adopt new technologies securely, particularly in markets with varying levels of cybersecurity maturity. How is the role of partners evolving as customers embrace AI, and where do you see the greatest opportunities and capability gaps within the EEMEA partner ecosystem?
Check Point operates through a 100% channel-led model, so our partners are fundamental to how we do business across EEMEA. Their role is becoming even more important as organisations adopt AI and modernise their infrastructure.
Customers increasingly need more than technology. They need trusted advice on how to introduce AI securely, understand their exposure, protect increasingly complex environments and translate security policies into practical controls. Partners are well positioned to provide that guidance because they understand local markets, regulatory requirements and the specific needs of businesses in their countries.
This creates opportunities across AI Security, Workspace Security, Exposure Management, Hybrid Mesh Network Security and managed services. There is also a growing opportunity for partners to move beyond individual technology deployments and build ongoing services that help businesses manage their security over time.
At the same time, the ecosystem needs to continue developing its capabilities around AI security, cloud environments and emerging technologies. EEMEA is too diverse for a one-size-fits-all approach. Our focus is on equipping partners with the technology, training and support they need to address these changing requirements and deliver the right outcomes for their markets.
- Looking beyond Engage Dubai 2026, what are your key strategic priorities for Check Point across EEMEA over the next 12 to 18 months? Which market developments, customer requirements or emerging opportunities do you expect will have the greatest influence on the region’s cybersecurity industry?
Over the next 12 to 18 months, our priorities will be centred on helping organisations secure their AI adoption, strengthen prevention and simplify increasingly complex security environments.
AI security will remain a major area of focus. Businesses across EEMEA want to take advantage of AI, but they need to protect the data, applications, users and agents involved. We will continue helping organisations secure AI across its lifecycle, from development and training through to deployment and everyday use.
We also see significant demand for a more unified approach to security. Organisations are operating across data centres, cloud platforms, SaaS applications, branch locations and remote workforces. Our focus on Hybrid Mesh Network Security, Workspace Security and Exposure Management reflects the need to apply consistent protection and prioritise the risks that matter most across these environments.
Alongside this, strengthening our relationships with customers and partners across individual markets will remain essential. The opportunities in EEMEA are significant, but success depends on understanding local requirements and having the right expertise close to the customer.
Our objective is straightforward: help businesses transform and grow securely. Cybersecurity should enable organisations to pursue new opportunities, not become an obstacle to them. Our ambition is to make cybersecurity an accelerator of transformation, not a constraint on it.